


How to Recover SEO of Hacked Sites?
Websites can occasionally be attacked or hacked. In such cases, Google may apply certain penalties to websites to protect users and provide a safer web experience. As a result, your site’s SEO performance may be negatively affected. In this article, I’ll share some recommendations on how hacked or compromised websites can recover their organic performance.
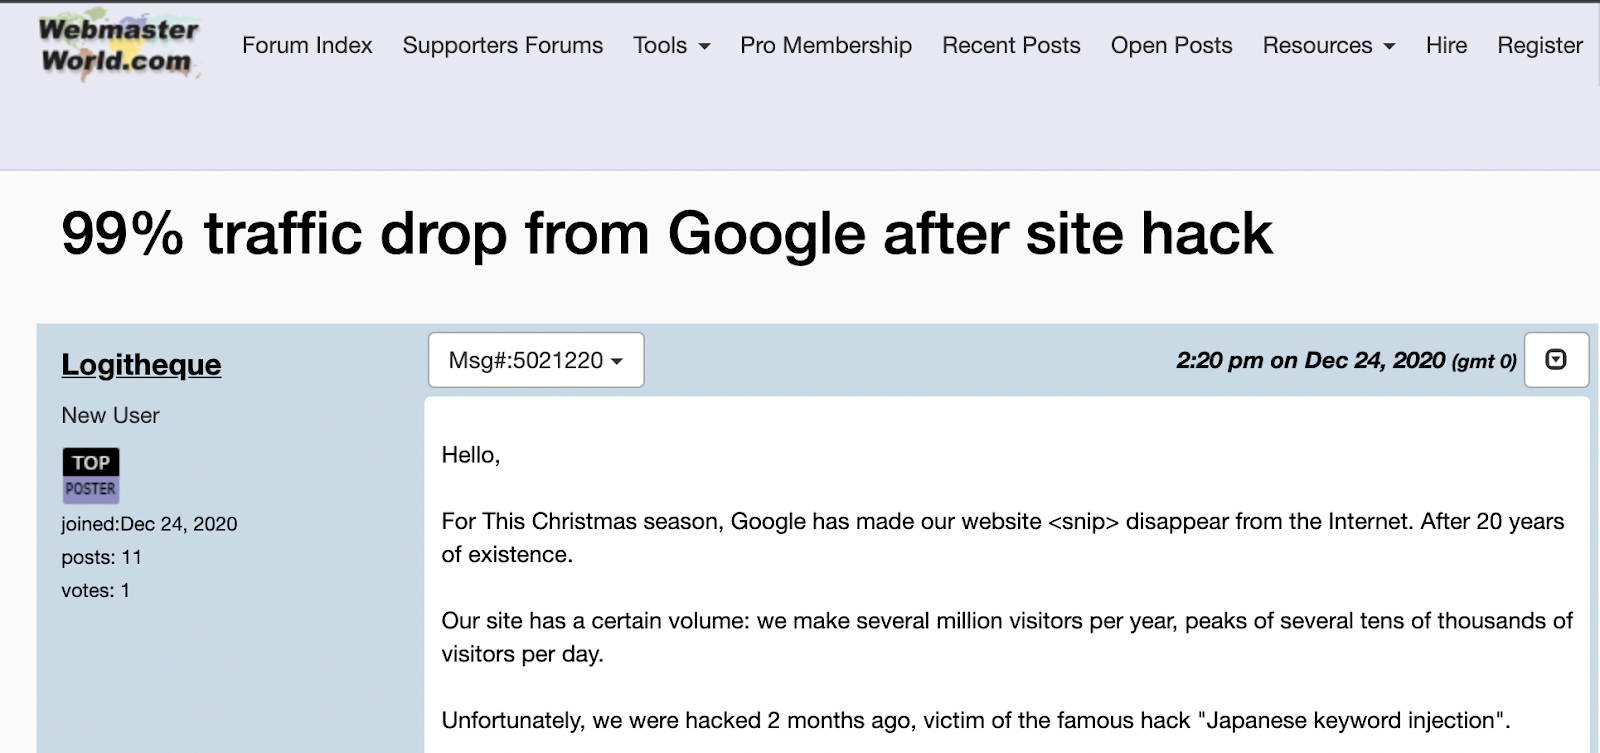
You can find many discussions on forums showing that traffic from Google dropped after an attack or a “hack”:
Because pages outside your control are created on your site, hundreds of thousands of pages may suddenly enter Google’s index. These pages may initially return a 200 status code and then redirect your visitors to the intended destination site with a 301. If you do not prevent this, many of these pages may remain on Google, as shown in the example image below:
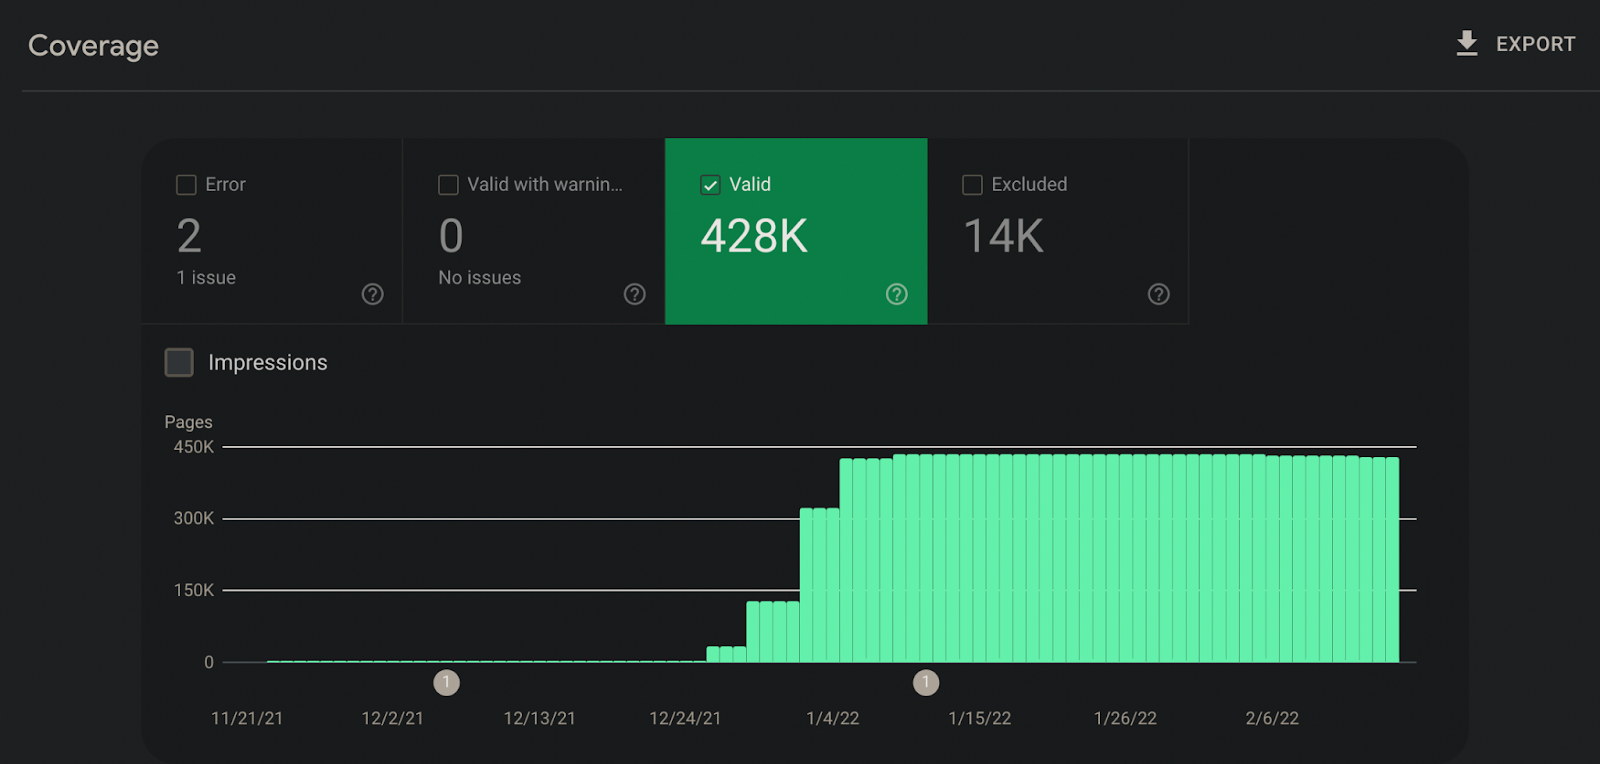
Even if you do not want these pages, Google may discover them more easily because ready-made CMS platforms can automatically add them to sitemaps. Even after you remove these pages from the sitemap, they may continue to remain in the index:
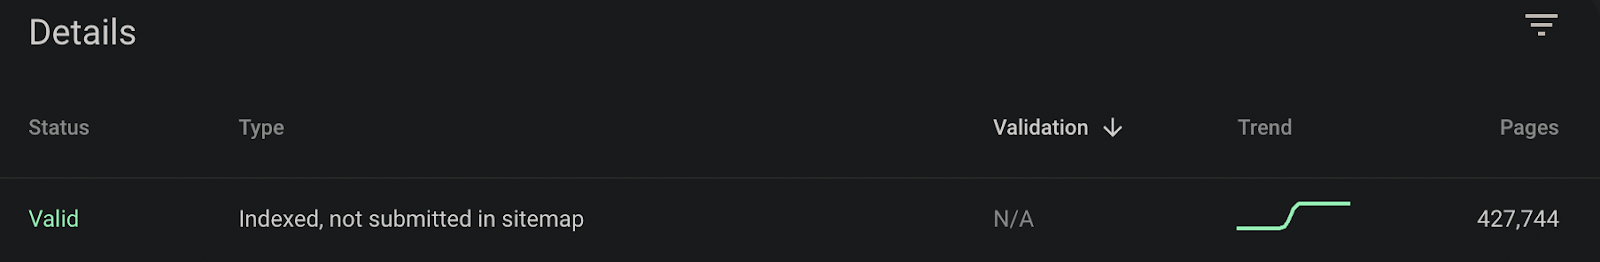
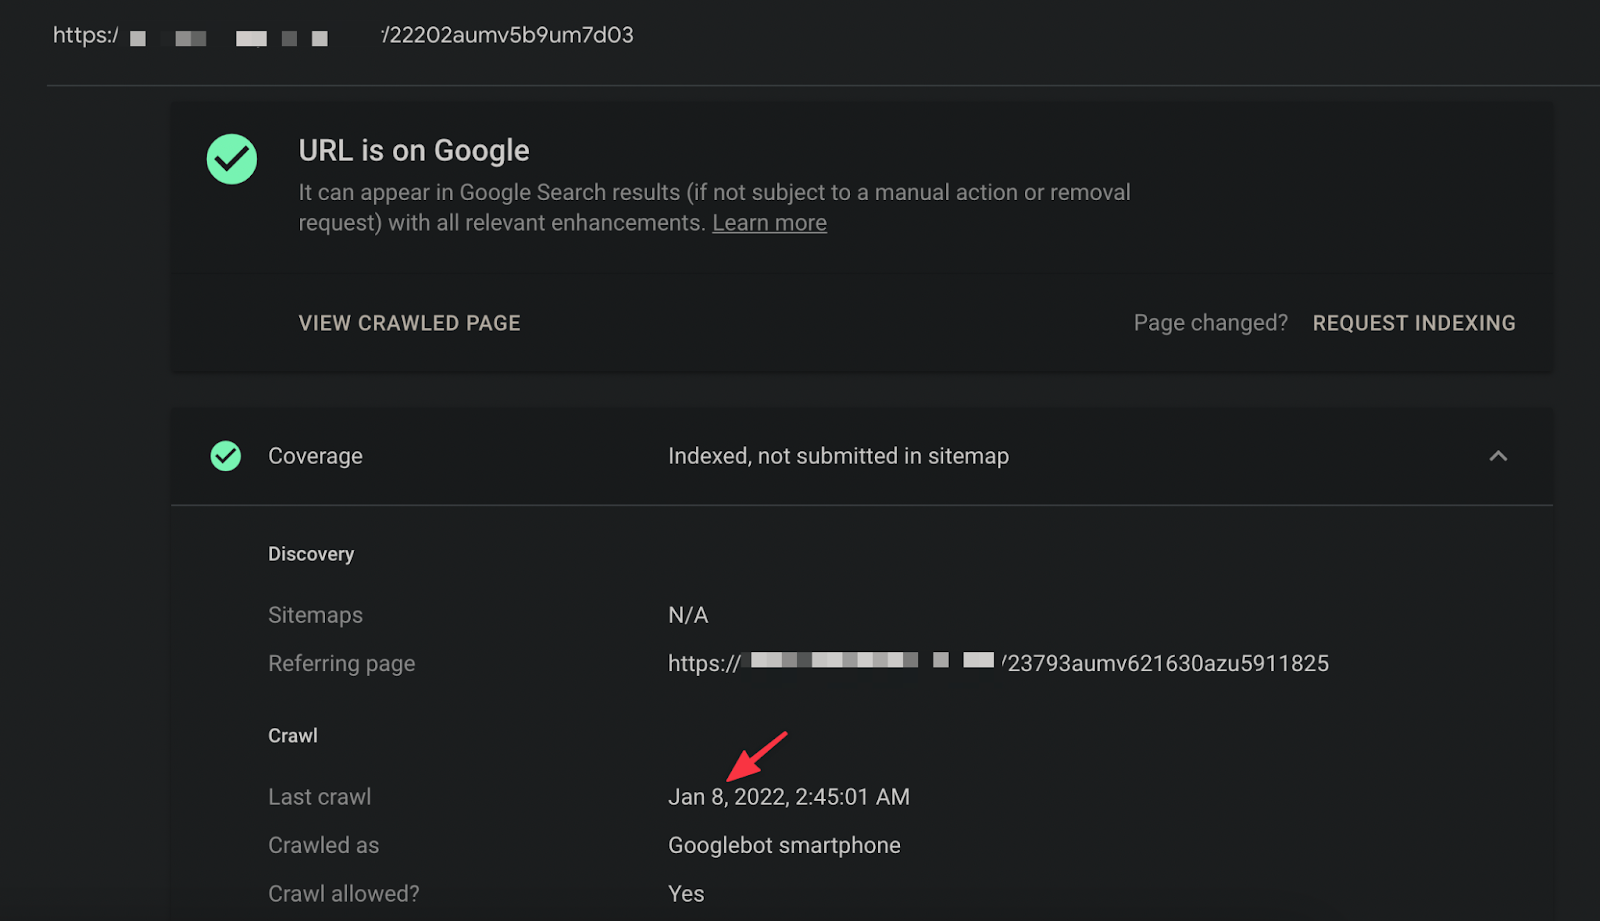
For the number of indexed URLs to decrease, Googlebot needs to crawl these pages again. Even if you remove the malware, you may still experience index optimization issues because Googlebot may not revisit those pages after the first time it discovered them.
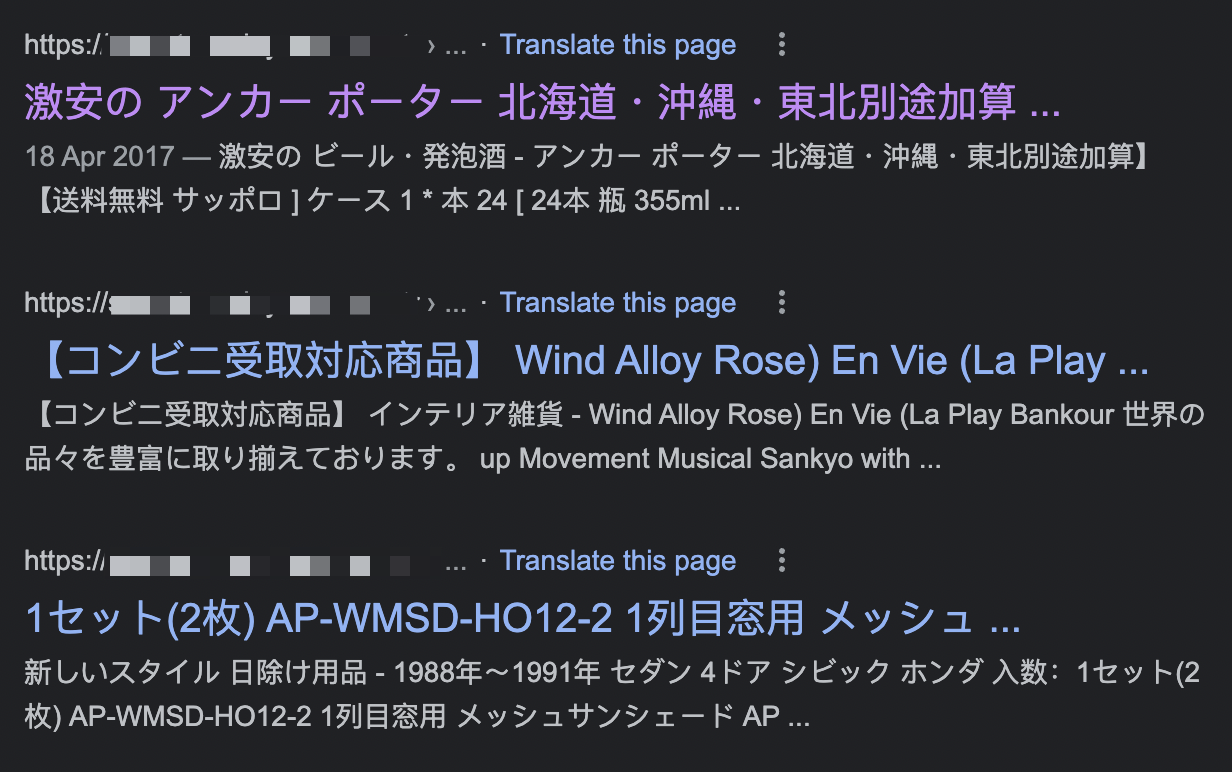
As you can see in the example below, pages resulting from Chinese or Japanese hacking attacks, which are well-known in the SEO community, can appear in the SERP:
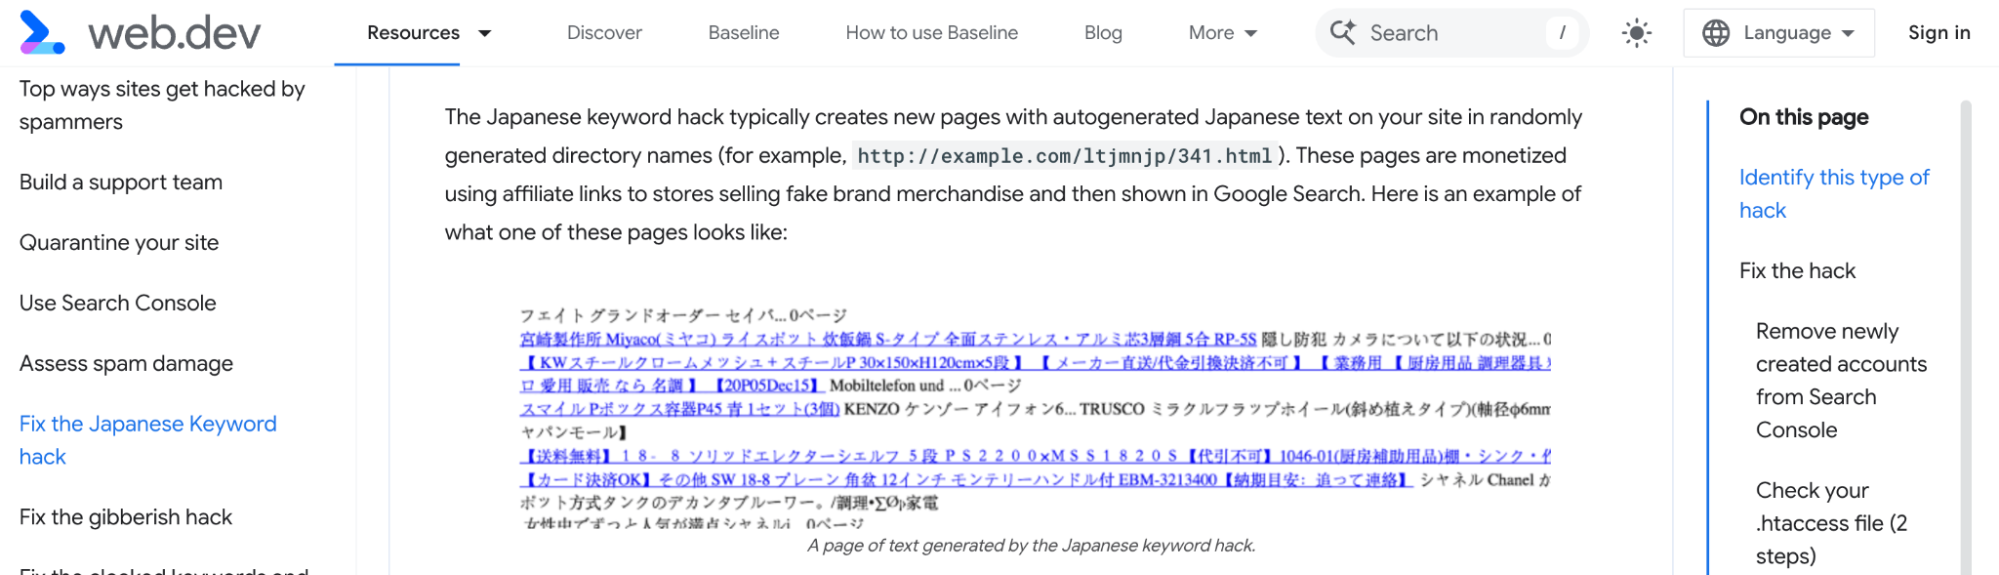
Google has also provided specific guidance for this type of attack here:
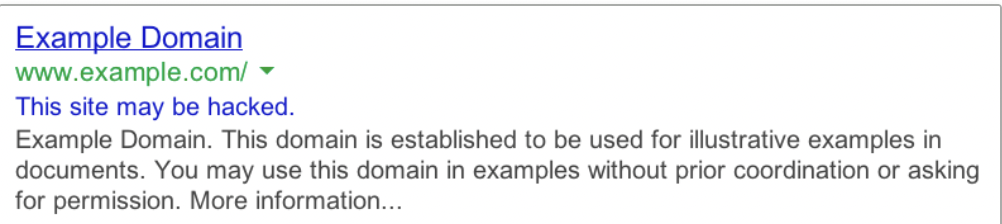
In addition, browsers such as Chrome may display warnings in the SERP such as “this site may be hacked” or “this site may harm your computer”:
You can report sites that Google has not discovered but that you believe may be harmful at https://safebrowsing.google.com/safebrowsing/report_phish/?hl=tr.
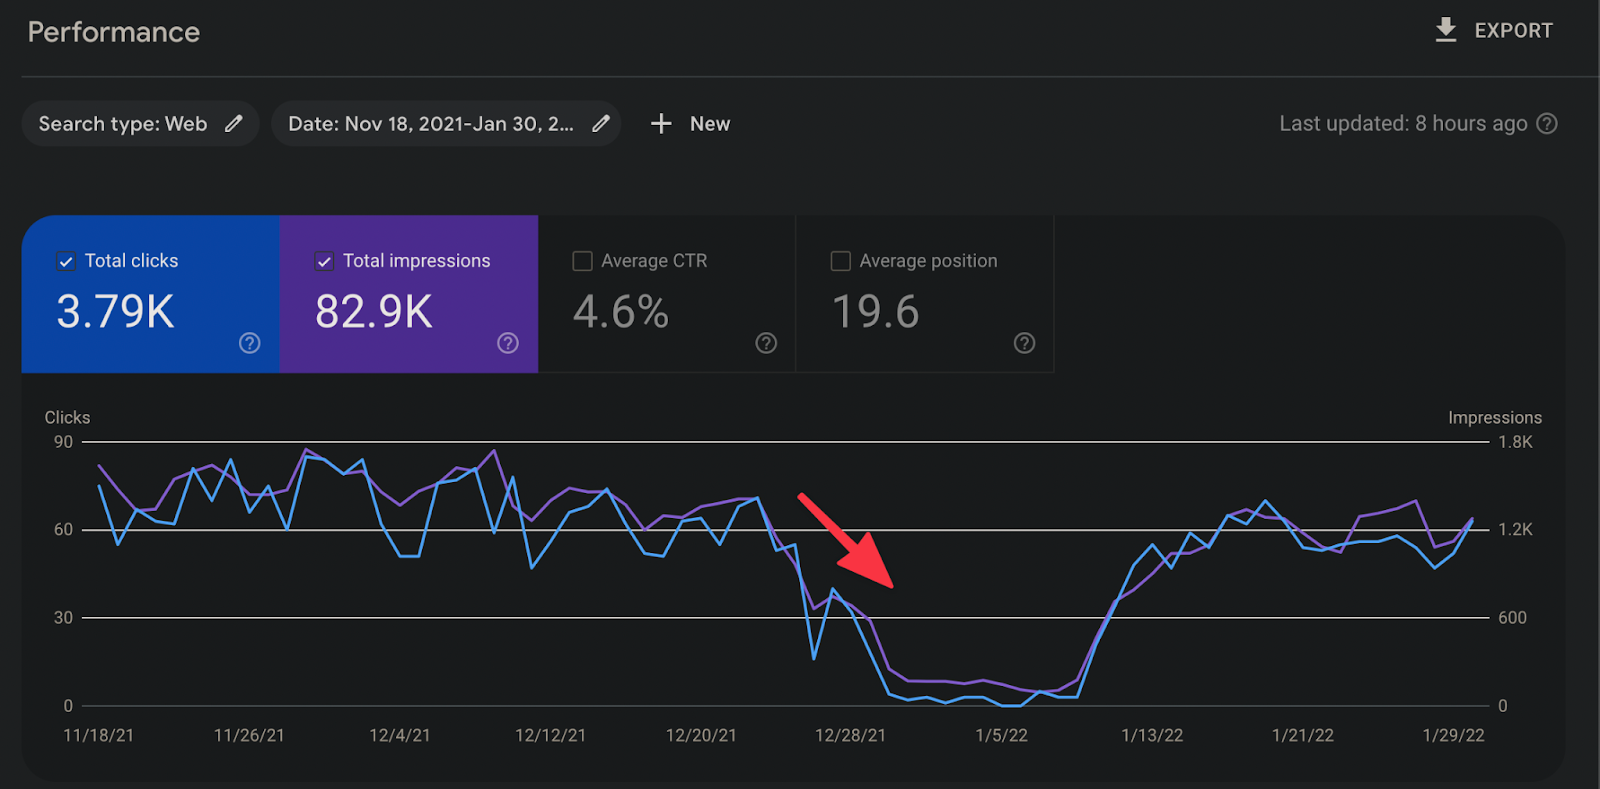
Google may not detect hacked or malicious pages, or it may not apply a manual action to your site. In such cases, it is important to carry out your own checks as well. In the example below, you can see how the SEO performance of an attacked or hacked website declined. It is also normal to see drops in Google News and Google Discover reports.
It is also worth checking whether the hacked pages are included in your sitemaps. You should review not only the sitemaps created for posts, but also sitemaps such as images-sitemap.xml.
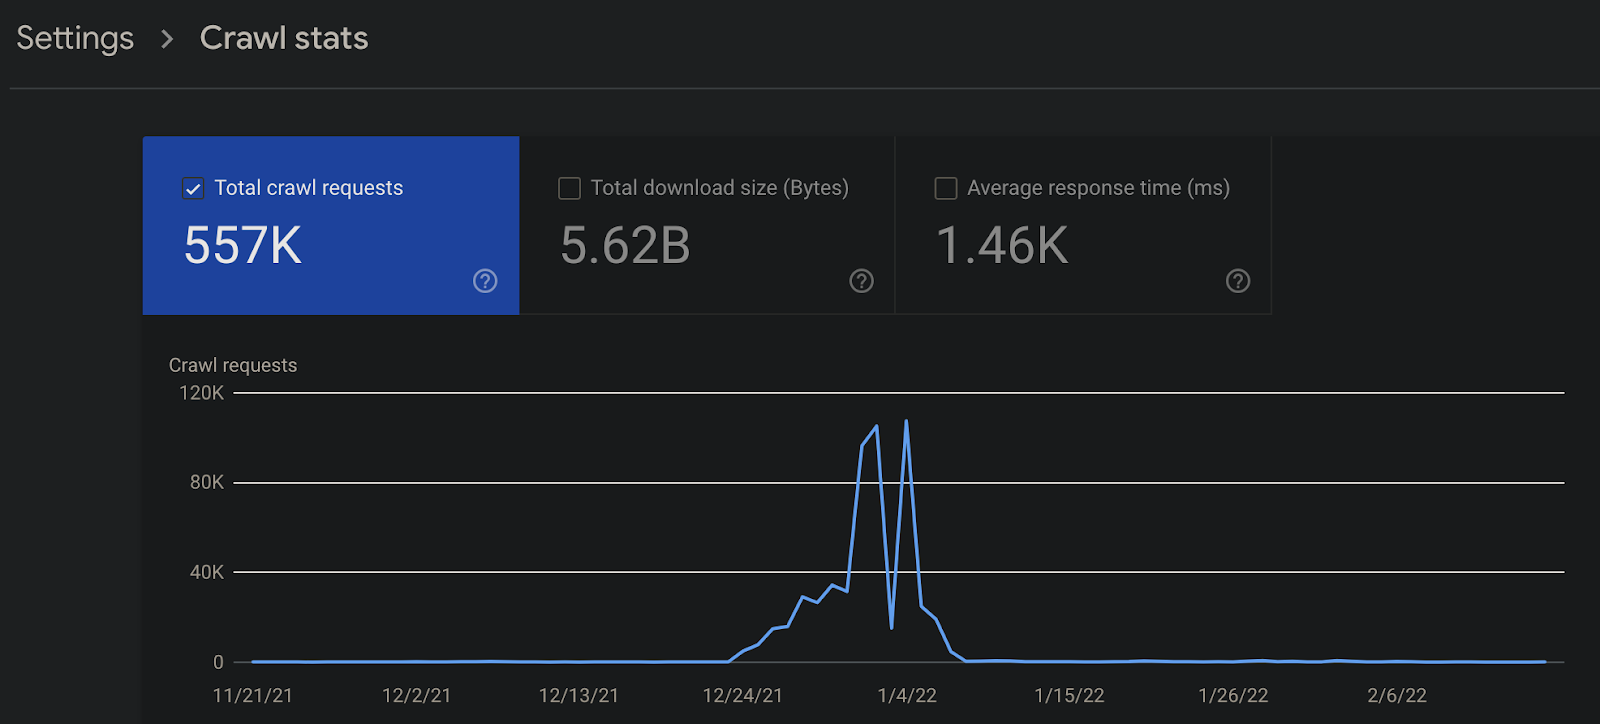
In the Crawl Stats reports, you can also identify how much crawl activity increased after the pages entered Google’s index and how much it decreased after the pages were removed. If you are experiencing a similar situation on your site, you should definitely review these important reports.
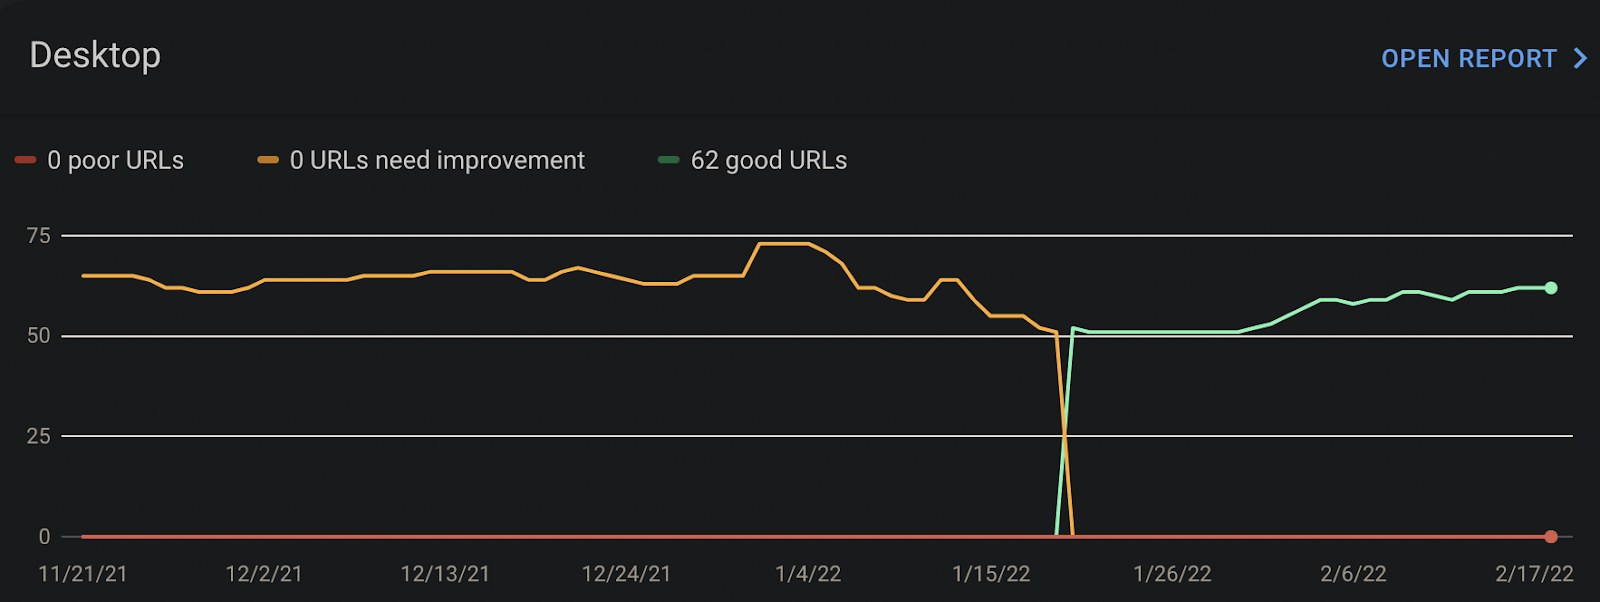
Your Core Web Vitals data may not be affected much in this situation. Since the data comes from the Chrome UX Report, the status of your indexed pages may still be reflected there.
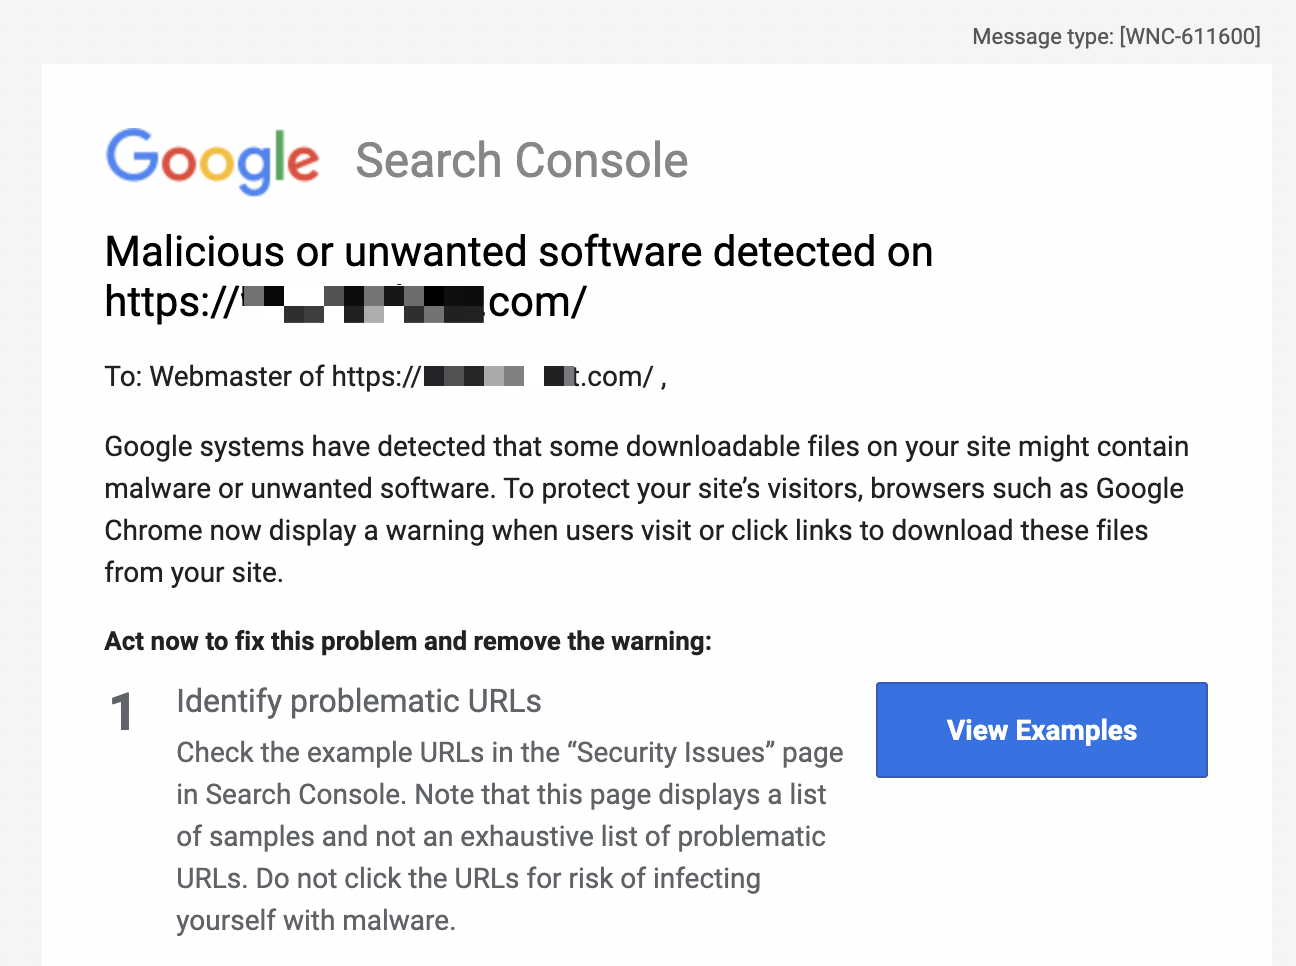
As I mentioned above, Google may not always send you an email or notification. When it does, you may receive a notification similar to the example below:
An example that can be found in Search Console is given below:
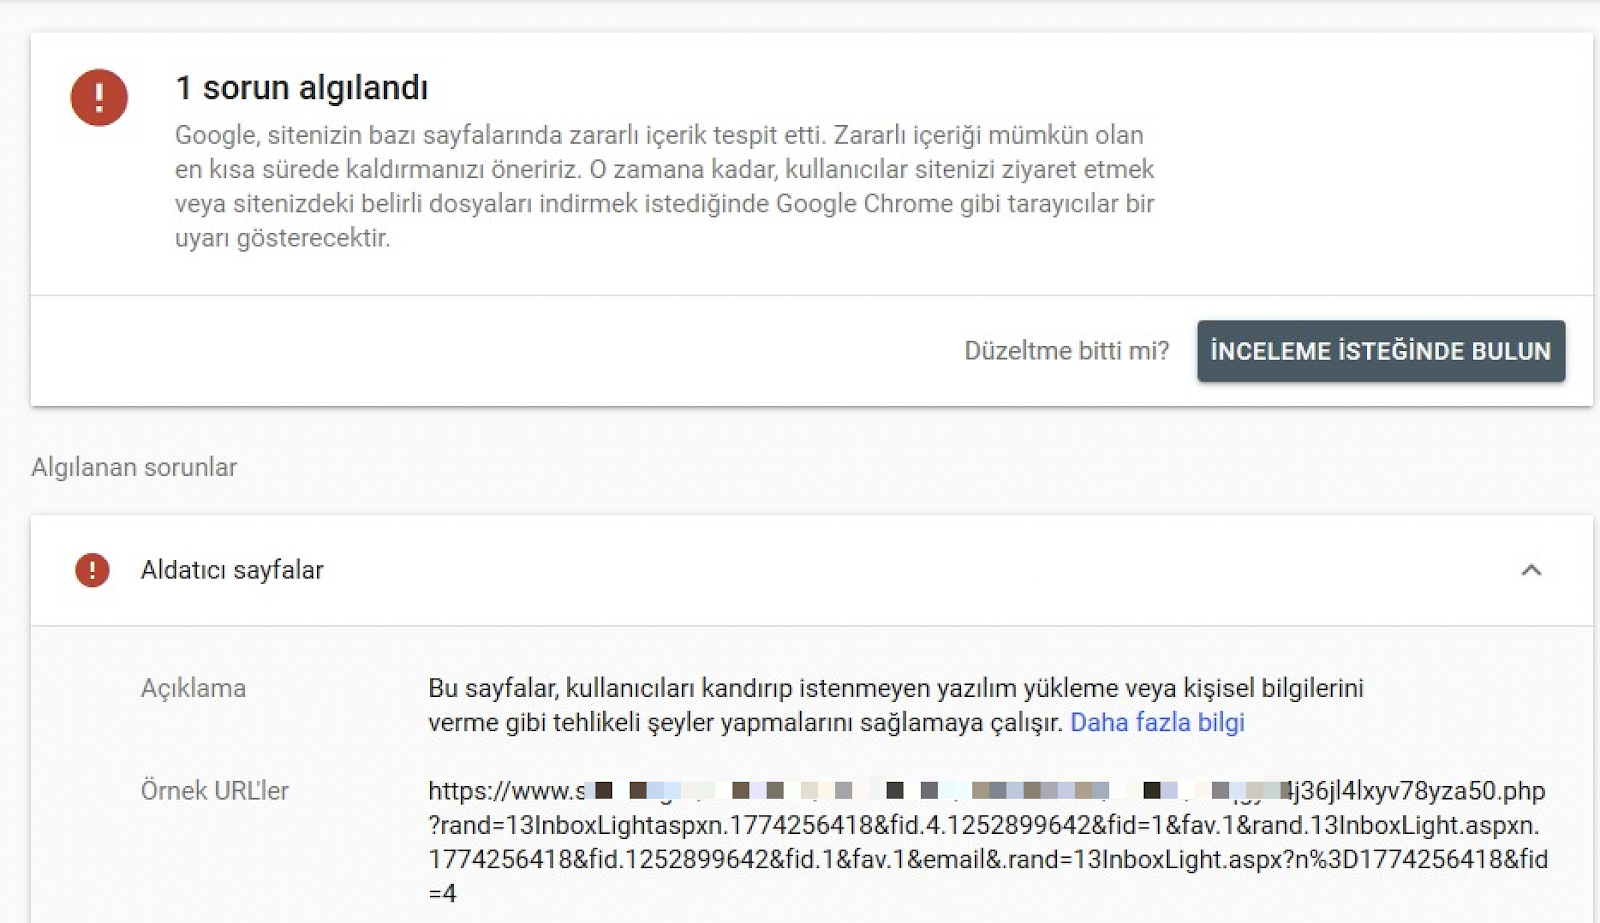
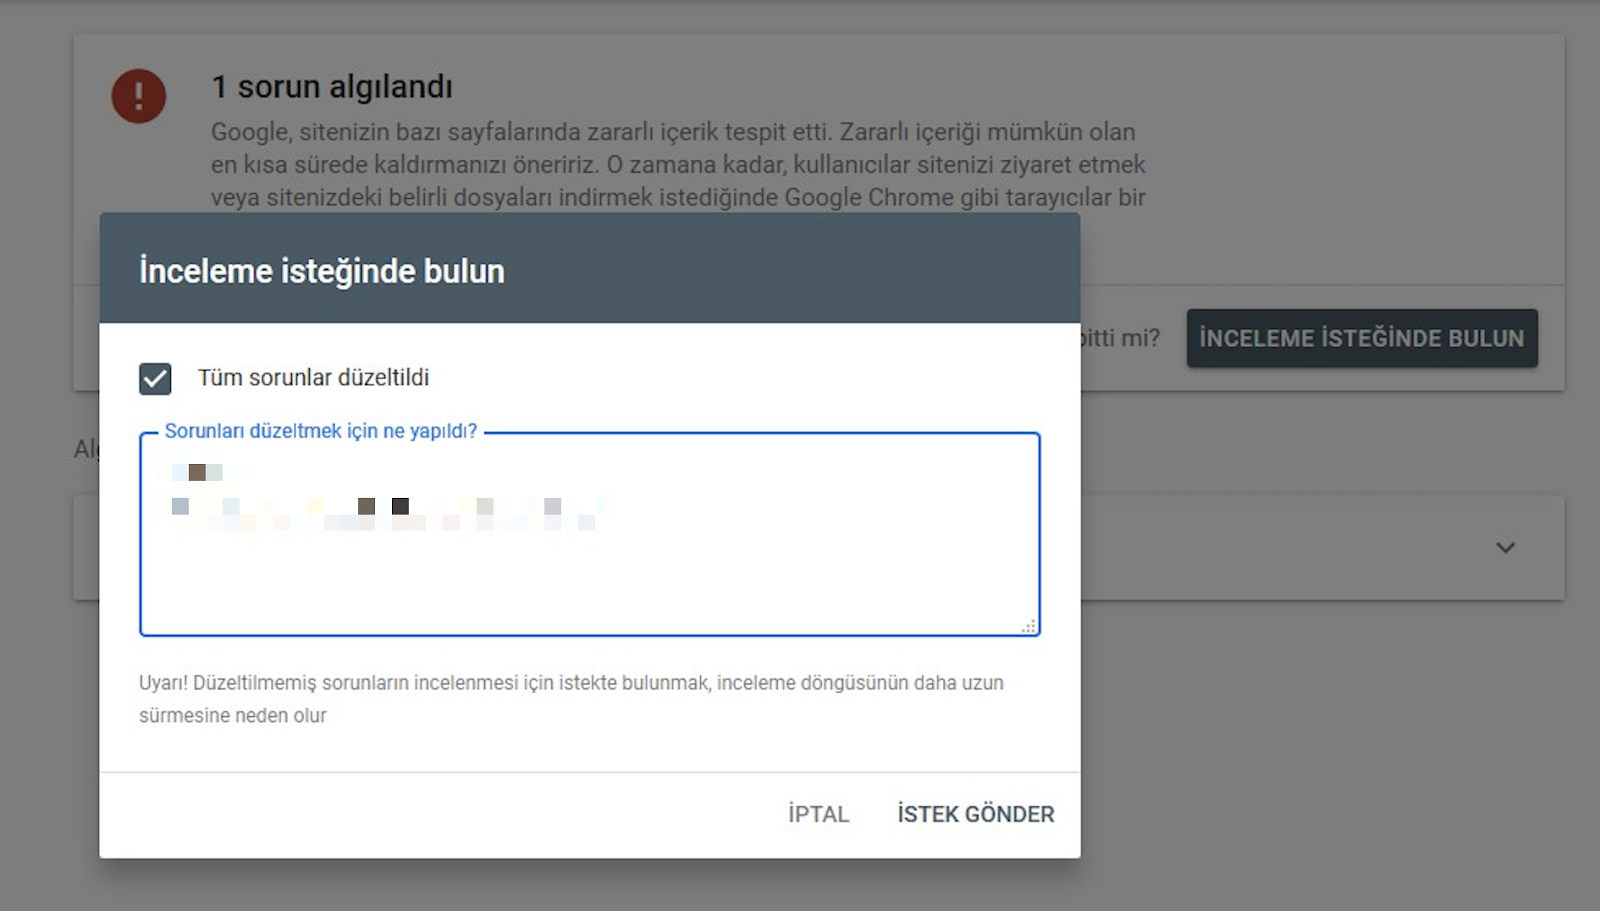
When you clean your site from viruses and deceptive pages, you should definitely request a review and write detailed procedures in the incoming form. If this notification belongs to the previous site owner, you can also indicate this situation in detail in the form. The manual process will be removed in a short time:
If I Secure My Site, Will I Regain Old SEO Performance?
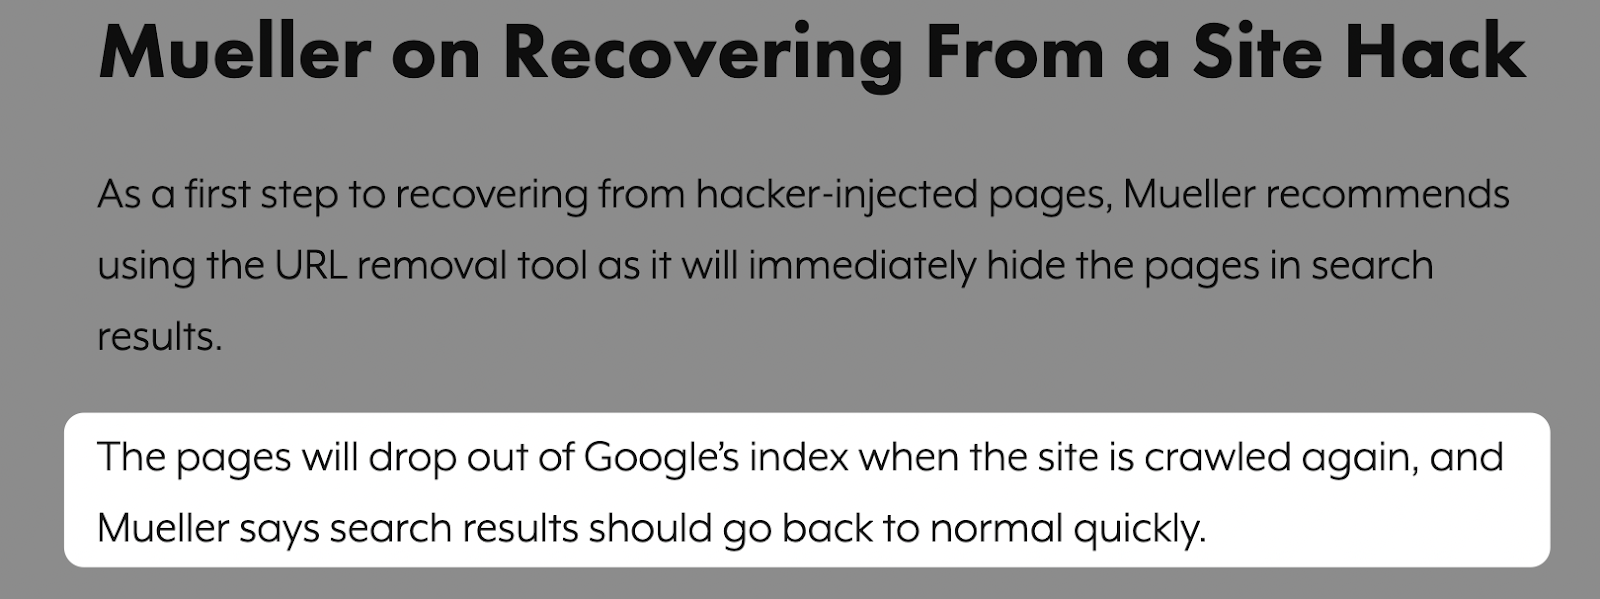
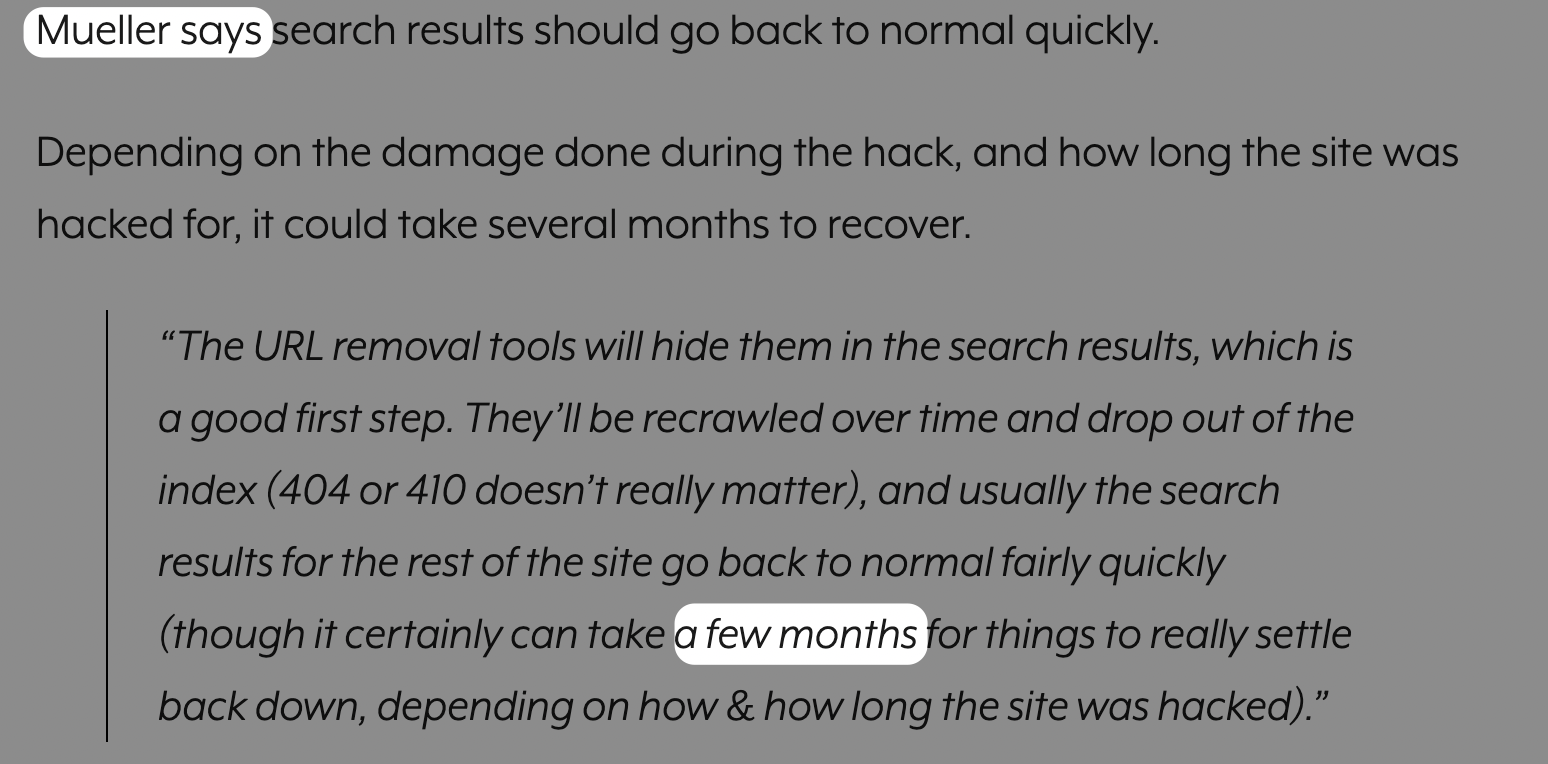
Yes, once you make your site more secure and Googlebot re-crawls your relevant pages, you can regain your performance over time. I would also like to note John Mueller's statement:
After How Many Months Will My Site's SEO Performance Come Back?
Depending on the size of your site, it may take a few months. If you have a URL structure that is rarely hacked, then you can think of it as a shorter period of time.
What Can Be Done to Clean Viruses and Recover Pages?
Removing and identifying malware or malicious pages is a separate area of expertise. For this, you can contact cybersecurity firms or specialized software companies, or you can reach out to us so we can identify the source of the problem and create a roadmap. At the very least, these efforts will help you take steps toward recovering your SEO performance.
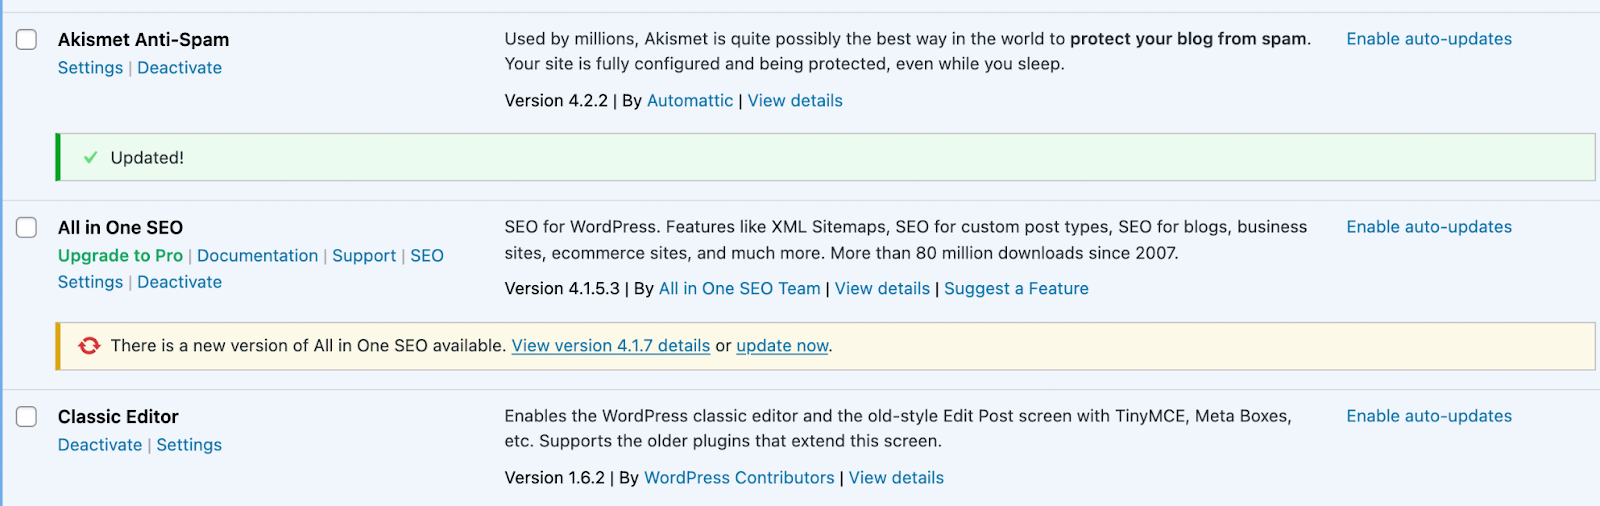
If you have a WordPress site, make sure your plugins are up to date and trustworthy. You can remove outdated and unnecessary plugins.
You can check if there are any users added to the dashboard other than you or your team. You should definitely change your password. In addition, you can set a custom administration panel path instead of the classic /wp-admin panel path:
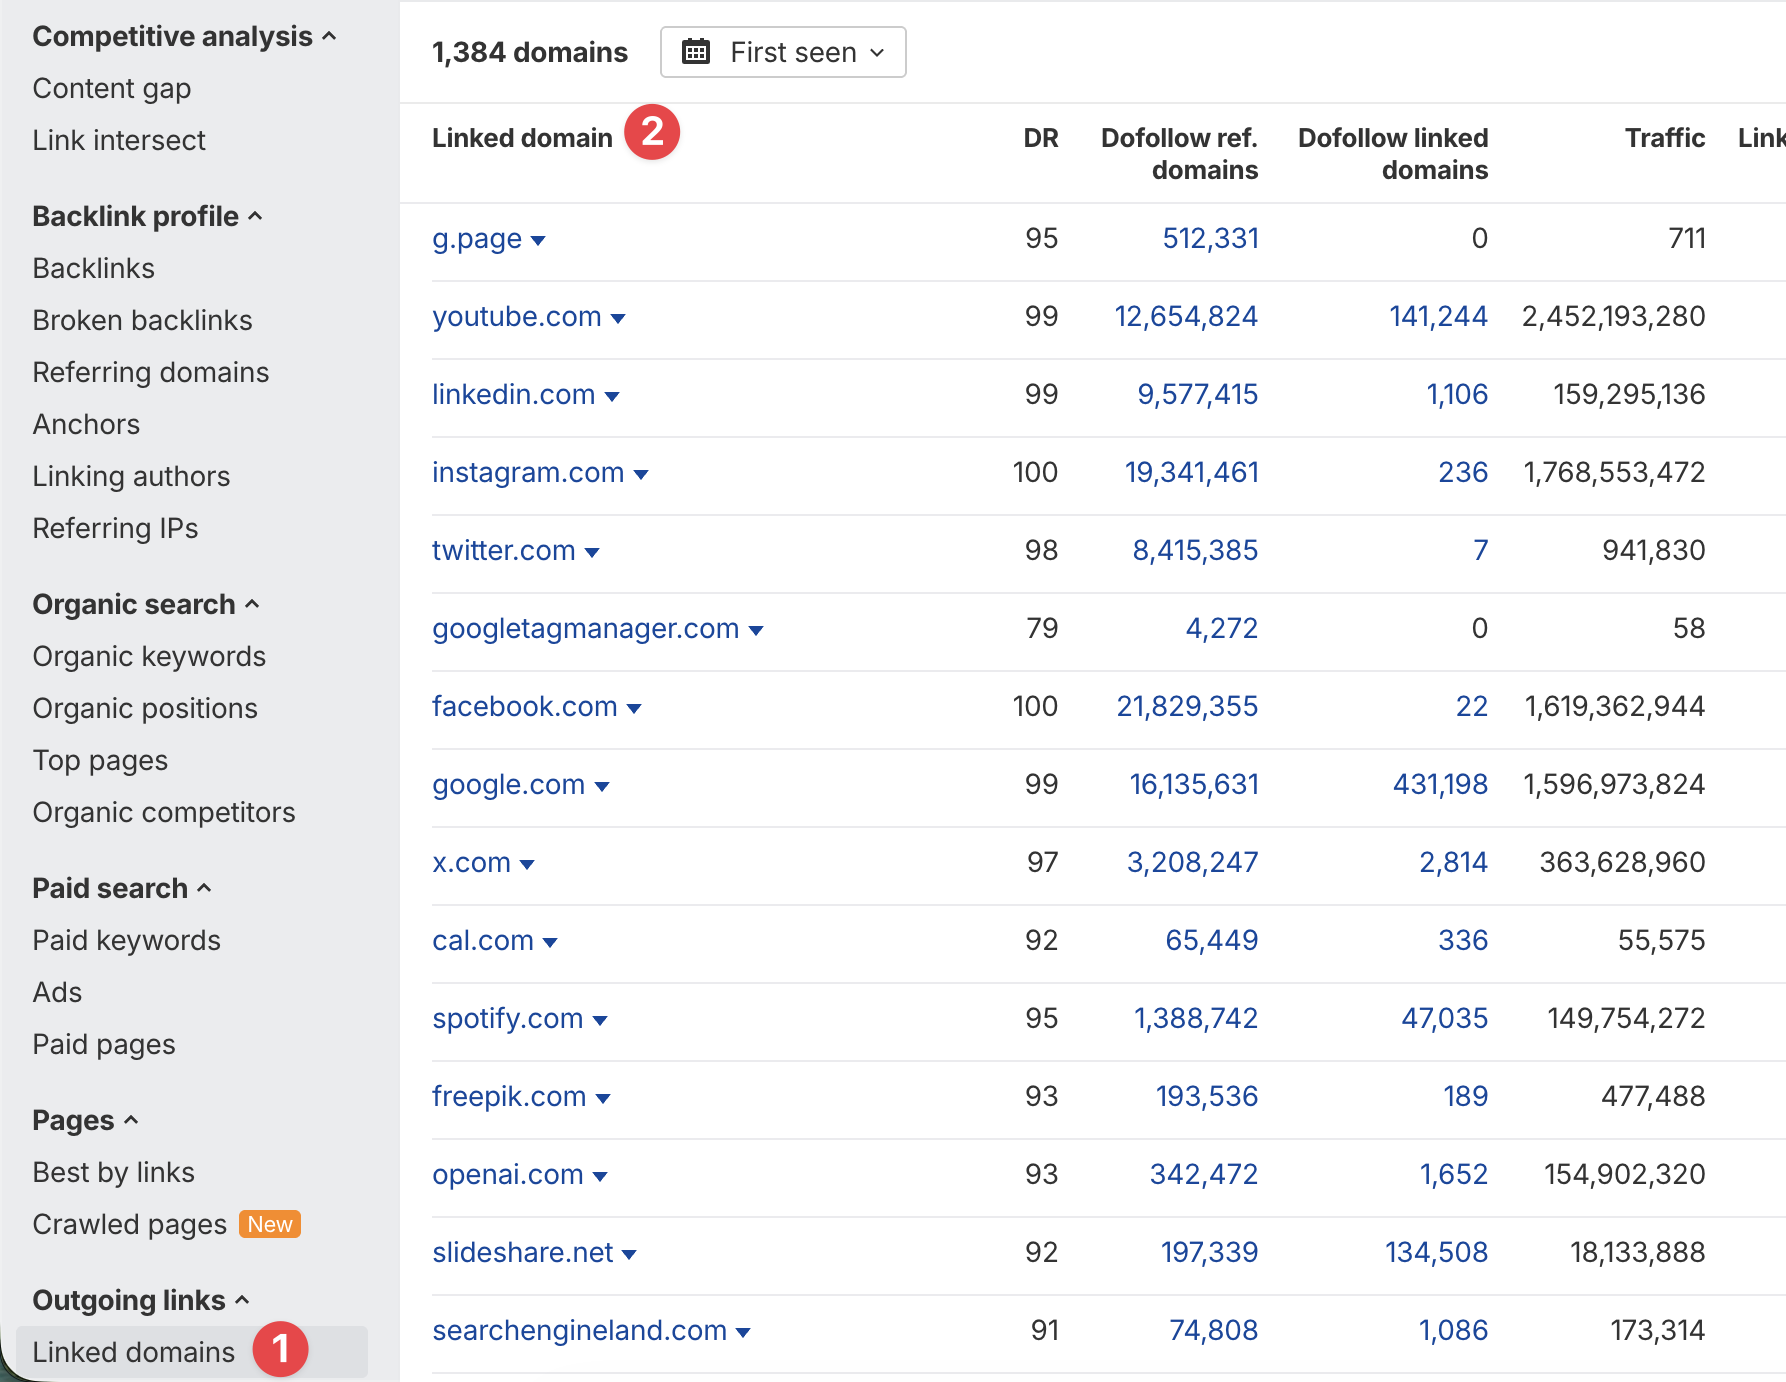
Using Ahrefs or a similar tool, you can identify links from your site to other websites. Since these links may not appear within posts or pages and can sometimes be added to files such as footer.php, these tools can provide you with a consolidated view. If you find outbound links that were added without your knowledge, open the relevant files and remove them.
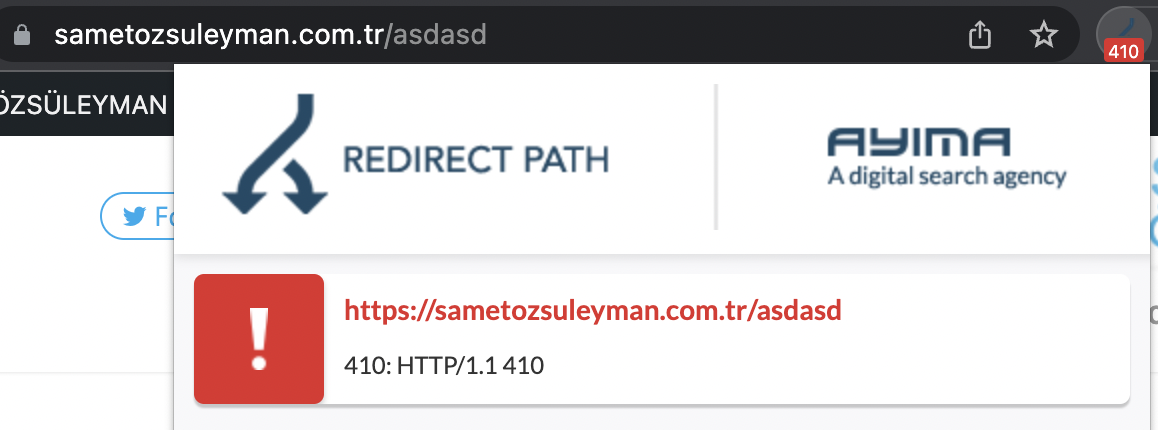
Delete redirected pages that are unrelated to your site and make sure they return a 404 or 410 status code:
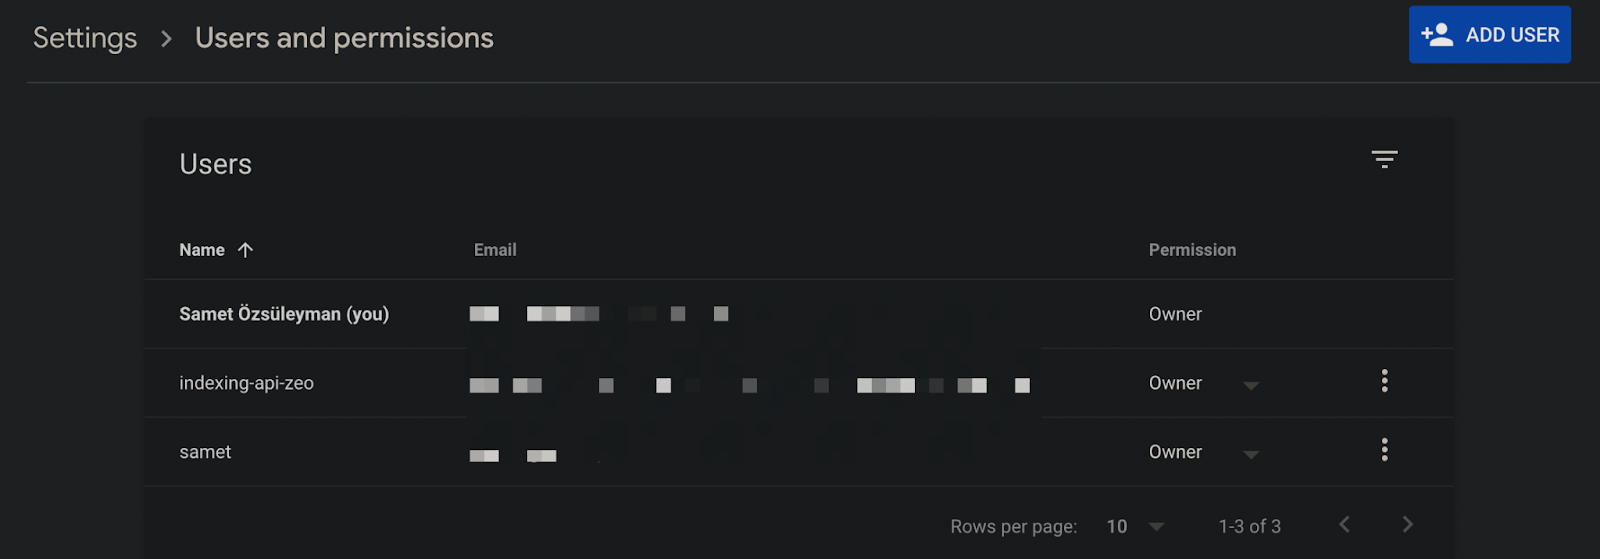
Check whether any other users have been added to your Search Console account. With a simple meta verification code added to the site, you could end up giving someone else access to your site’s entire performance data.
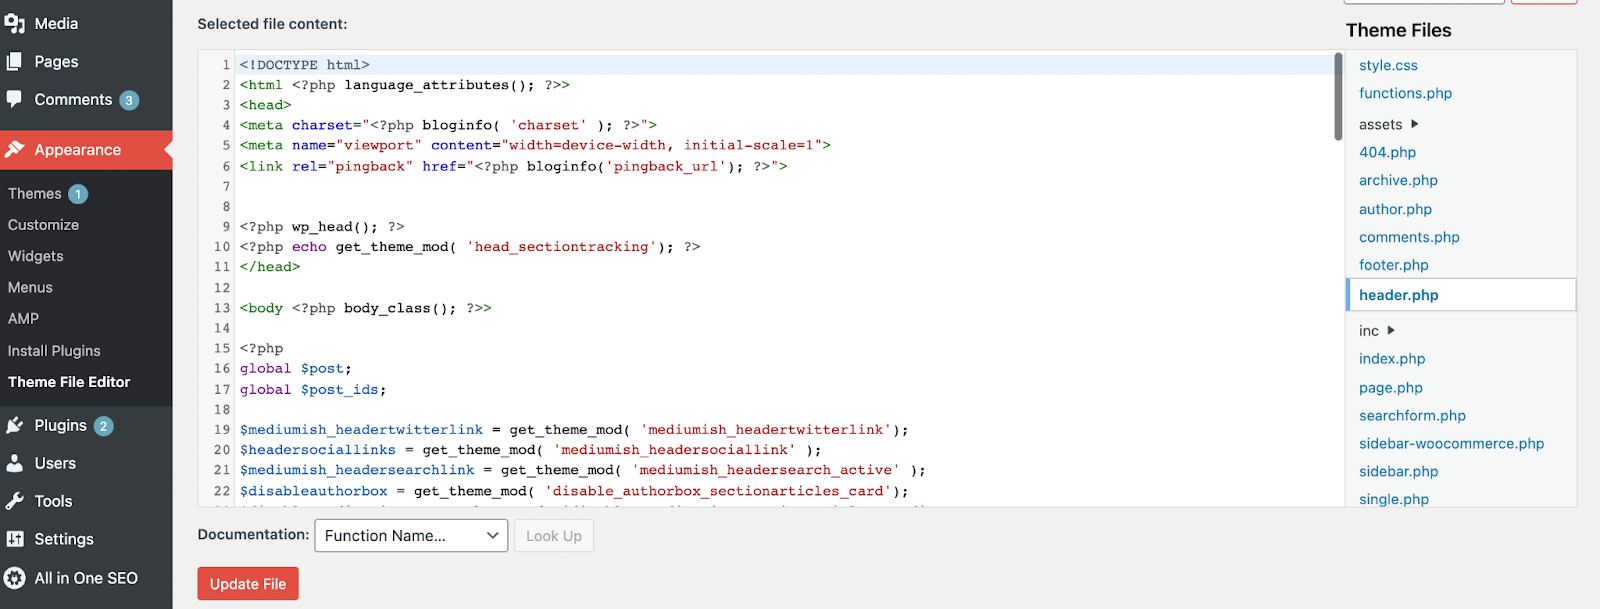
Update your themes and check whether any files have been modified. If you find any code blocks that were added without your knowledge, remove them. Of course, don’t forget to create a backup before making these changes.
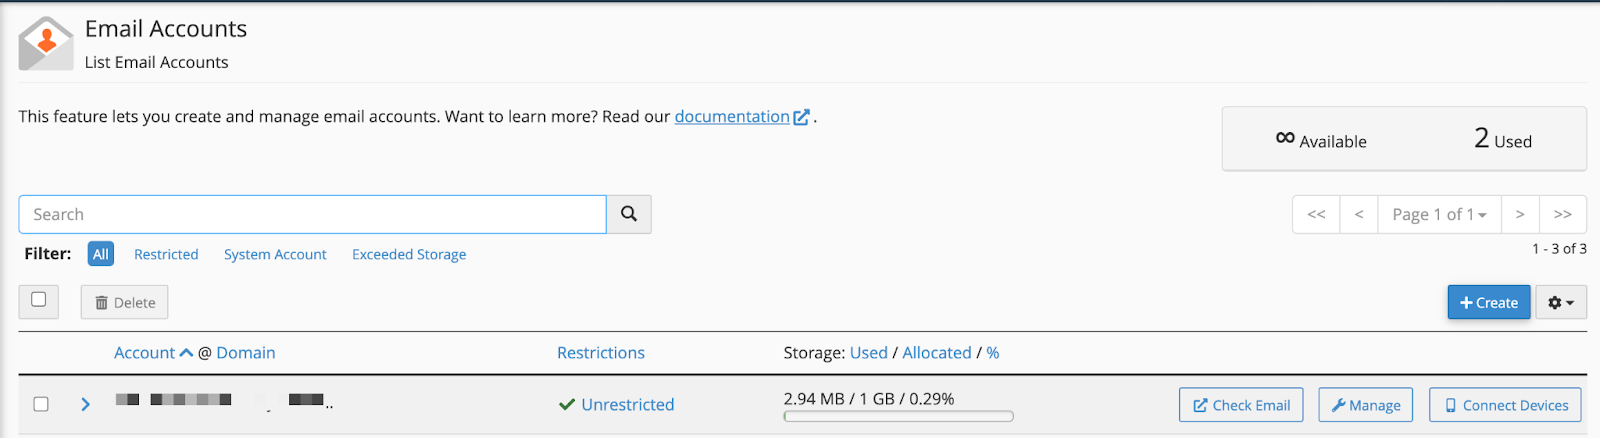
If you use a control panel such as cPanel, check for any email accounts that may have been created without your knowledge. These email addresses could be used to access your site’s services without your awareness and may cause your site to return 5xx status codes. After all, your site has limited disk space and bandwidth.
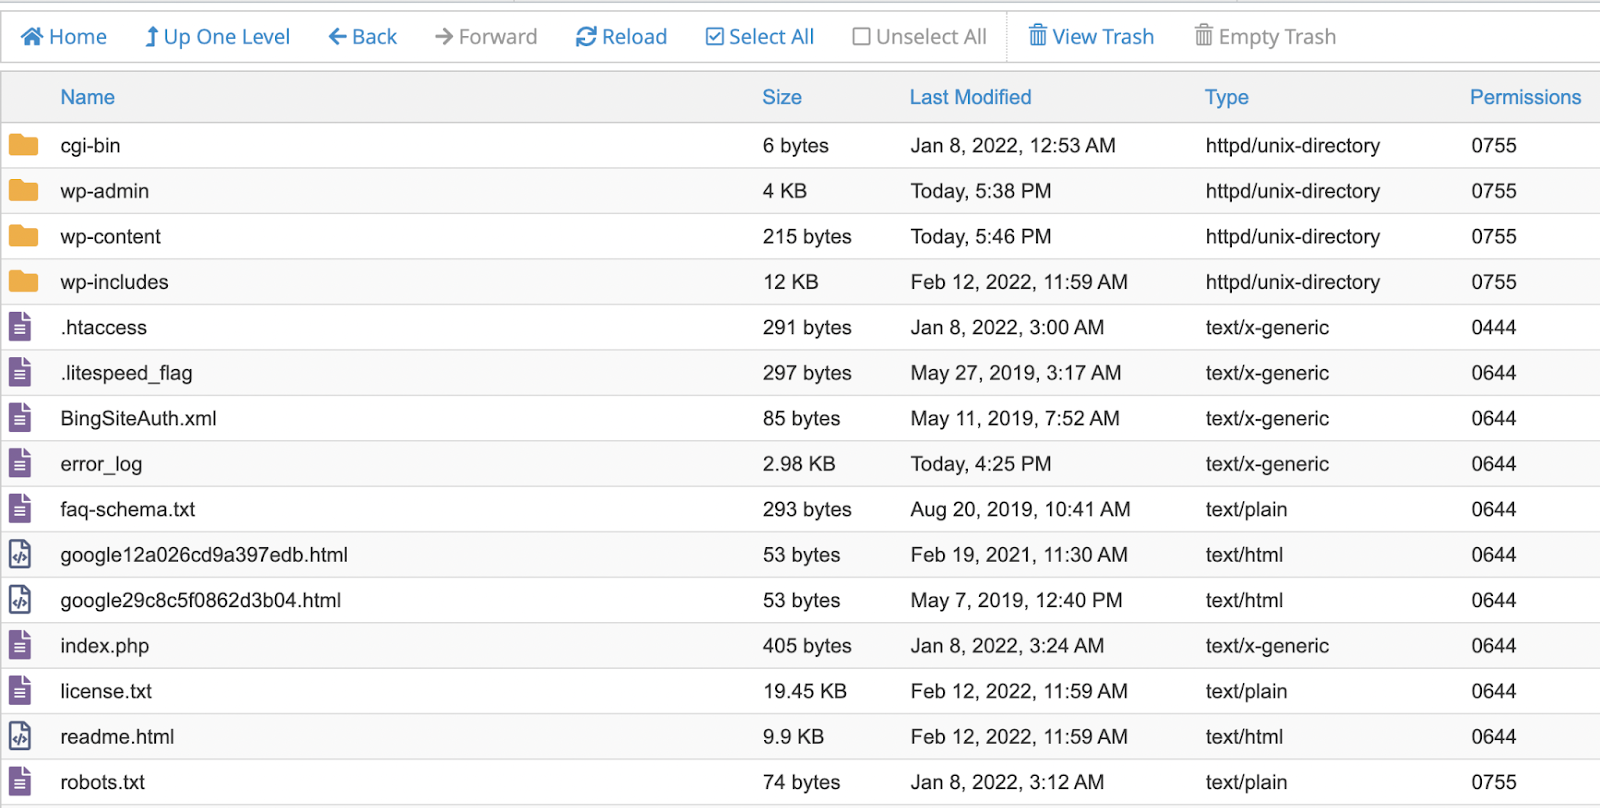
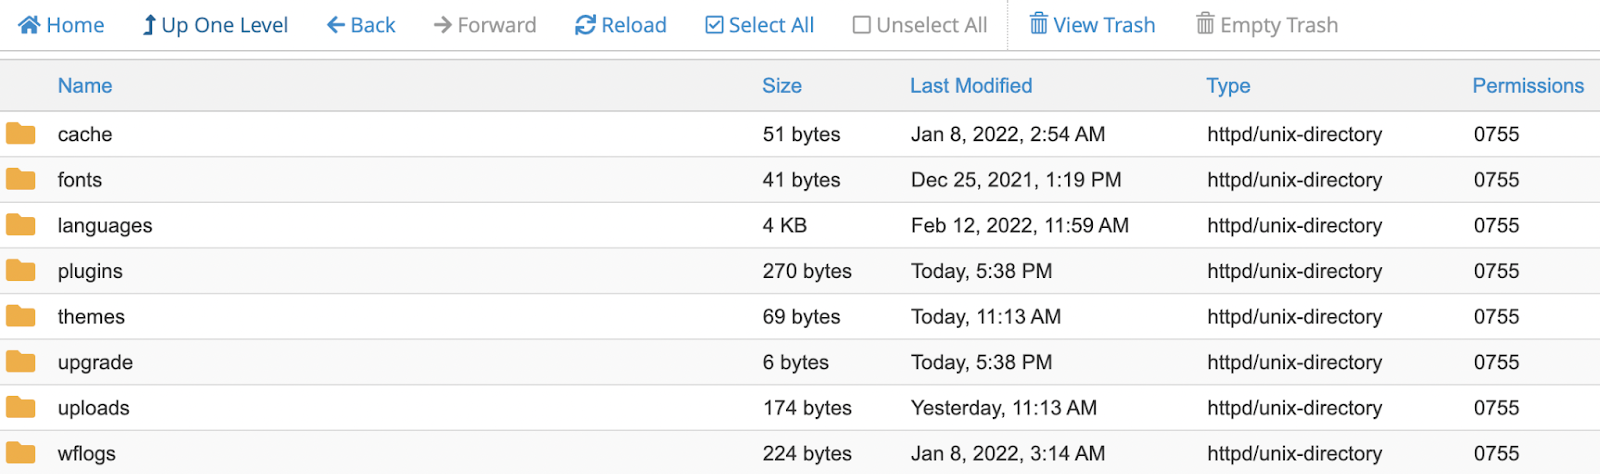
Access all of your website files via an FTP program or cPanel File Manager. By checking the “Last modified” information, you can review files that were changed recently. You can also remove files that were added under unusual names or created with names very similar to existing files.
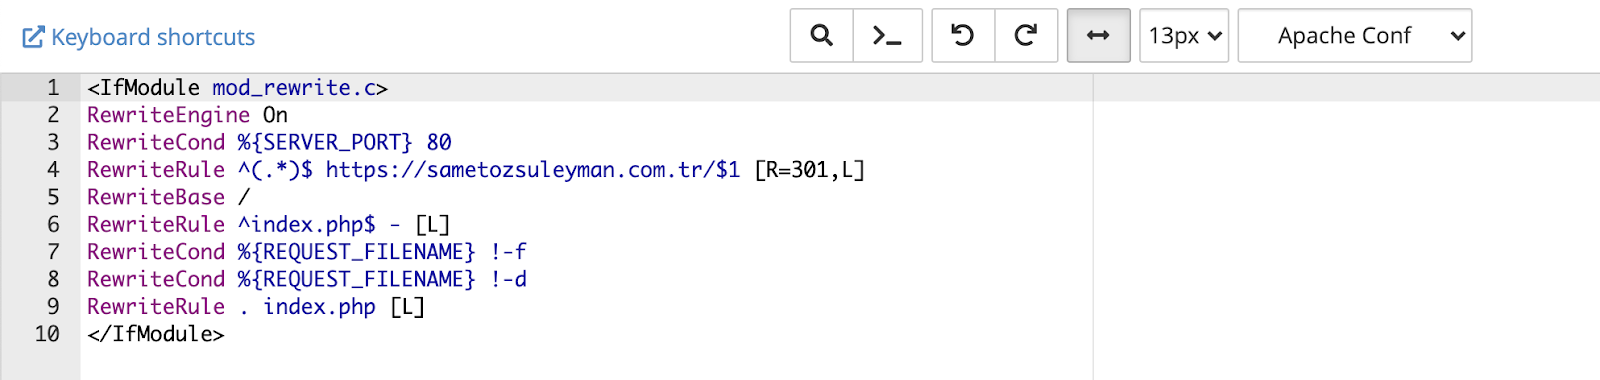
Check your .htaccess file. Since many redirects are managed there, review the code and remove any redirect rules that send users to unfamiliar or unrelated addresses. After making the changes, check all versions of your site, including www/non-www and HTTPS versions.
Always manually inspect the contents of subfolders. Consider examining different file types as well as files that look suspicious to you:
As stated in Google’s documentation, you can quarantine your site while carrying out these steps. You can redirect your site to a different page that returns a 503 response code. Taking the site offline can help reduce the risk to your users and prevent visitors from being affected. Blocking these pages with Robots.txt alone is not sufficient, as visitors may still be able to access them.
As I wrap up this article, I would like to emphasize that this is a serious situation and that both the potential issues and the remediation process can take time. Following the types of incidents I have broadly grouped under the term “hack,” your visibility in organic and AI results may be negatively affected, your revenue may decline, and your competitors may move ahead of you. Recovering from these drops can also be costly.
I recommend making sure your site is secure and taking precautions at every point where you believe it could be vulnerable to an attack. Wishing you malware-free and spotless SEO projects :)
Useful Links:


